Skip to contentNewCVE credited by Microsoft

Web application and API security

Penetration testing, on demand.

Manual web application and API testing by a researcher with a public record. Scoped to what you ship, with every finding proven and every fix retested.

  • Manual-first testing
  • Written authorization
  • One retest included
Illustrative engagement

app.example.testWeb + API

  1. 01Scope
  2. 02Authorize
  3. 03Test
  4. 04Report
  5. 05Retest

Finding 01 · HighFixed, retest passed

Invoice API returns records from other tenants

Fictional target and finding, shown to illustrate the process.

Vulnerabilities reported through programs run by

See the public sources
  • Microsoft
  • NASA
  • Dropbox
  • Mastercard
  • Dell Technologies
  • T-Mobile
  • Twilio
  • United Airlines
  • Lenovo
  • LastPass
  • Tripadvisor
  • Rakuten
  • Seagate
  • Under Armour
  • Keeper Security

Public bug bounty and disclosure programs, not clients. None endorses ZeroDay Labs. Logos are trademarks of their owners.

Credited CVE

Microsoft credited our lead researcher.

Full track record

MicrosoftAzure Front Door

CVE-2026-118742

Azure Front Door Elevation of Privilege Vulnerability

Microsoft's description: Incorrect permission assignment for critical resource in Azure Front Door (AFD) allows an unauthorized attacker to elevate privileges over a network.

CVSS 3.1 base score

8.6/ 10

High · Microsoft rates it Important

Vendor
Microsoft
Weakness
CWE-732
Published
Exploited
No

Researchers

The people behind the testing.

Full track record
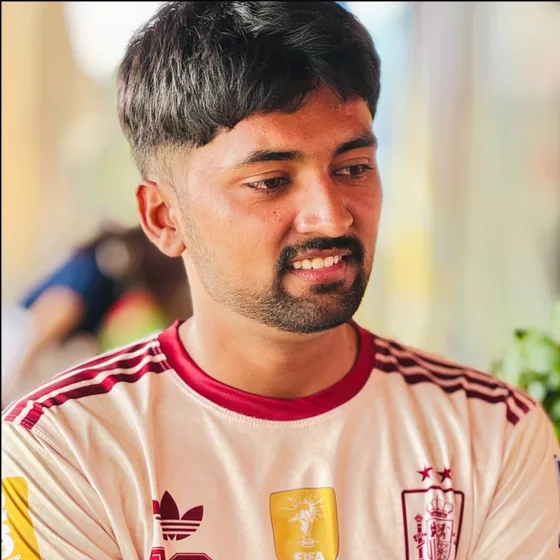
Portrait of Muhammad Waseem

Lead security researcher

Muhammad Waseem

Active in bug bounty and vulnerability disclosure programs since 2022, with a CVE credited by Microsoft, MSRC acknowledgments and a letter of appreciation from NASA.

Bugcrowd, as of 9 Nov 2026

#518
All-time rank1,399 points
513
VulnerabilitiesAcross 62 programs
97th
P1 percentile
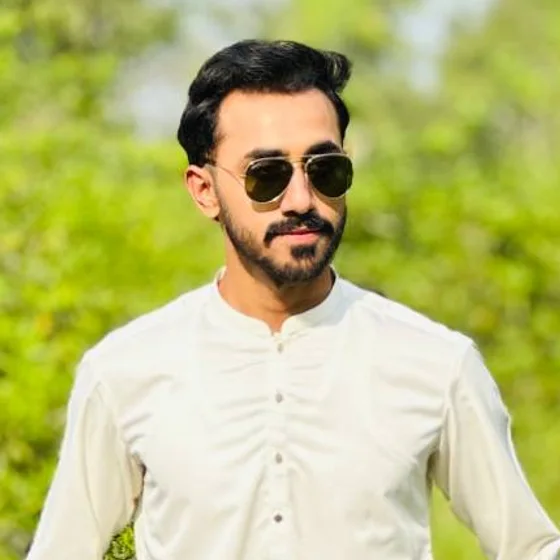
Portrait of Muhammad Shoaib Anwar

Security researcher

Muhammad Shoaib Anwar

Ethical hacker and cyber security analyst focused on penetration testing and vulnerability assessment, with findings reported through programs including Asana, Dropbox and Indeed.

Bugcrowd, as of 10 Nov 2026

#3440
All-time rank
33
Vulnerabilities
65th
P1 percentile

Earned through public vulnerability disclosure and bug bounty programs. These organizations are not clients of ZeroDay Labs and do not endorse it.

Services

Testing for the software you ship.

All services

Why ZeroDay Labs

Built the way real bugs get found.

01

Manual first

Tools support the work. A person decides what matters and proves it.

02

Scoped and tested by the same person

Nothing is lost between the conversation about your system and the test of it.

03

Proof, not noise

A finding is reported only when it is confirmed, with evidence your developers can act on.

04

Authorized, always

No testing starts without written permission and agreed rules.

How it works

From first message to closed findings.

Full process
  1. 1ScopeYou describe what to test. Targets, roles and timing are agreed, and you receive a written quote.
  2. 2AuthorizeThe system’s owner signs written authorization and rules of engagement. Testing does not begin without them.
  3. 3TestHands-on testing inside the agreed window. A critical issue is reported as soon as it is confirmed.
  4. 4ReportEvery finding comes with severity, business impact, evidence and a specific fix.
  5. 5RetestOnce you have fixed the issues, they are tested again and the report is updated with the results.

What you receive

A report your developers can use.

The report is written for two readers: the people deciding what to fix first, and the developers fixing it.

  • 01Executive summary
  • 02Scope and method
  • 03Findings by severity
  • 04Fix guidance
  • 05Retest results

Illustrative example · Fictional targetHigh

Invoice API returns records from other tenants

Affected
Invoice lookup endpoint, api.example.test
Impact
Any signed-in user can read invoices that belong to other organizations.
Evidence
Requests from two test accounts in separate tenants, with data redacted.
Fix
Check ownership on the server for every invoice lookup, and add a regression test.
Retest
Access denied across tenants. Finding closed.

Coverage

Where testing goes deepest.

01

Authentication bypass

Login flows, session handling and the assumptions between them.

02

Broken access control & IDOR

Object references and role checks that hold until someone asks twice.

03

Remote code execution

Deserialization, injection and the routes from input to process.

04

API security

Undocumented routes, mass assignment and inconsistent authorization.

05

JWT security

Signature validation, key handling and token audience.

06

Privilege escalation

Moving from a low-trust position to one the design never intended.

07

Web application security

Parser differentials, proxies and the gaps between layers.

08

Business logic

Workflows, limits and state changes used in ways the design never intended.

Questions

Before you get in touch.

All questions
How much does a pentest cost?

Each engagement is priced after scoping, based on the size of the application, the number of roles and the depth you need. You receive a written quote before anything starts.

How long does it take, and how soon can it start?

Both depend on scope and current availability. The start date and test window are confirmed in writing with your quote.

Who performs the testing?

The person who scopes your engagement performs the testing. The lead tester’s public record is on the About page, with links to the original sources.

Is retesting included?

Yes. One round of retesting is included after you fix the reported issues, and the report is updated with the results.

Can you test production?

Yes, under agreed rules. Staging is preferred where it matches production, and actions that could disrupt service are excluded unless you agree to them in writing.

Find it before someone else does.

Tell ZeroDay Labs what you need tested. You will get a clear scope and a written quote before any work begins.
Request a pentest